How iApp E-Voting Keeps a Ballot Secret with an Election Key Pair
· 2 min read

iApp E-Voting protects the secrecy of the ballot with a pair of keys made for each election: a public key that seals ballots, and a private key that opens them on counting day.
Corrected 12 October 2026
An earlier version of this post said the system used blockchain technology and four synchronised database copies that made tampering "virtually impossible". It does not use blockchain, and we have removed those claims. This post now describes what the system does.
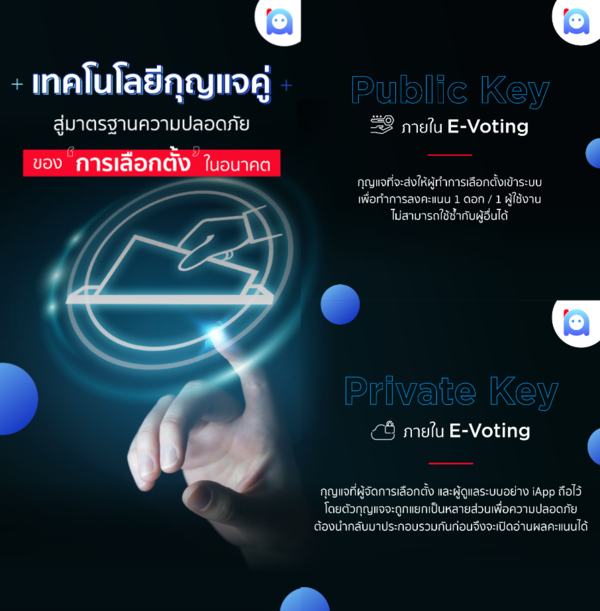
Two keys, made for one election
- The public key seals ballots. Each ballot is encrypted in the voter's own browser with the election's public key before it is sent.
- The private key opens ballots. It is needed only on counting day, to decrypt the ballots before they are counted.
The committee holds the private key
- The committee can make the key pair offline, on a machine that is not connected to the network.
- The private key can be split into up to five shares held by different committee members, and a set number of them must come together on counting day to decrypt the ballots.
- Decryption and counting take place on counting day, in front of the committee.
What each voter can check
After voting, each voter receives a receipt number and a QR code. On the status page they can check that the ballot was received and, on counting day, that it was decrypted for the count.
For more about iApp E-Voting: iApp E-Voting